Picture a Tuesday morning. An MSP technician pushes a script through the RMM to a 15-person accounting firm. By the time the coffee is finished, every machine in that office is protected by Prisma Browser for Business, analyzing pages as they load, scanning every file, watching every extension.
The MSP didn’t have to purchase another console to make it happen. Licensing, provisioning, deployment and configuration is all managed in the Guardz platform, thanks to its partnership with Palo Alto Networks.
Why this combination works
Palo Alto Networks built Prisma Browser for Business for small companies. It runs on Precision AI, the same security engine behind Palo Alto Networks’ enterprise platform. Every day those engines analyze over 5 billion events, block over 30 billion attacks, and identify hundreds of thousands of new malicious files and URLs. Inside the browser session, pages are analyzed as they render, files are scanned before they land and malicious extensions are blocked on sight.
Guardz extends these capabilities to its MSP partners so they can, in turn, better protect their client base. Activate and configure from Guardz, deploy via RMM/MDM and let top-tier browser security do the heavy lifting. Watch browser events correlate in the same incident as email, identity and the endpoint, so your team and the Guardz 24/7 MDR have the telemetry they need to stop threats. One account, one bill, one support path regardless of the number of clients you support.
Palo Alto secures the session. Guardz transforms it into a security operation.
“Browser is the core workspace for small businesses, where business apps, AI tools, and sensitive data converge,” said Shivam Srivastava, VP Product at Palo Alto Networks. “Working closely with Guardz, Prisma Browser for Business delivers a secure workspace that stops advanced threats, safeguards data, and controls the use of AI across your organization.”
The threats this is actually for
The Guardz research team has been documenting what is landing in browsers right now. Adversary-in-the-middle (AiTM) phishing relays the real login page. It looks correct because it is correct, and the session token is taken after MFA completes. Browser-in-the-browser attacks render a fake sign-in popup inside a legitimate page. HTML and JavaScript smuggling assembles malware inside the browser, so the endpoint never sees a download arrive.
Then, there’s the one that ties browser risk to AI risk. In a man-in-the-prompt attack, a malicious or compromised extension rewrites an employee’s prompt the moment before it sends, slipping in hidden instructions and copying business data. The request rides the employee’s own signed-in session, so network and data-loss tools see an approved person using an approved tool.
Every one of these completes within a browser session, which is precisely where most stacks have nothing watching.
One attack, one incident
Here is where the Guardz-Palo Alto Networks partnership sstarts changing your Tuesday.
- A phishing email gets through.
- The employee clicks.
- Prisma Browser for Business blocks the page as it renders.
In Guardz, that block is joined to the email it came from, the identity activity in the client’s Microsoft 365 and the endpoint the person was working on. One incident is generated, focused on one person with evidence from four places already attached, and the Guardz 24/7 MDR team is looking at the same picture.
Attackers never silo their attacks. Your stack finally does not either.
AI your clients can actually use
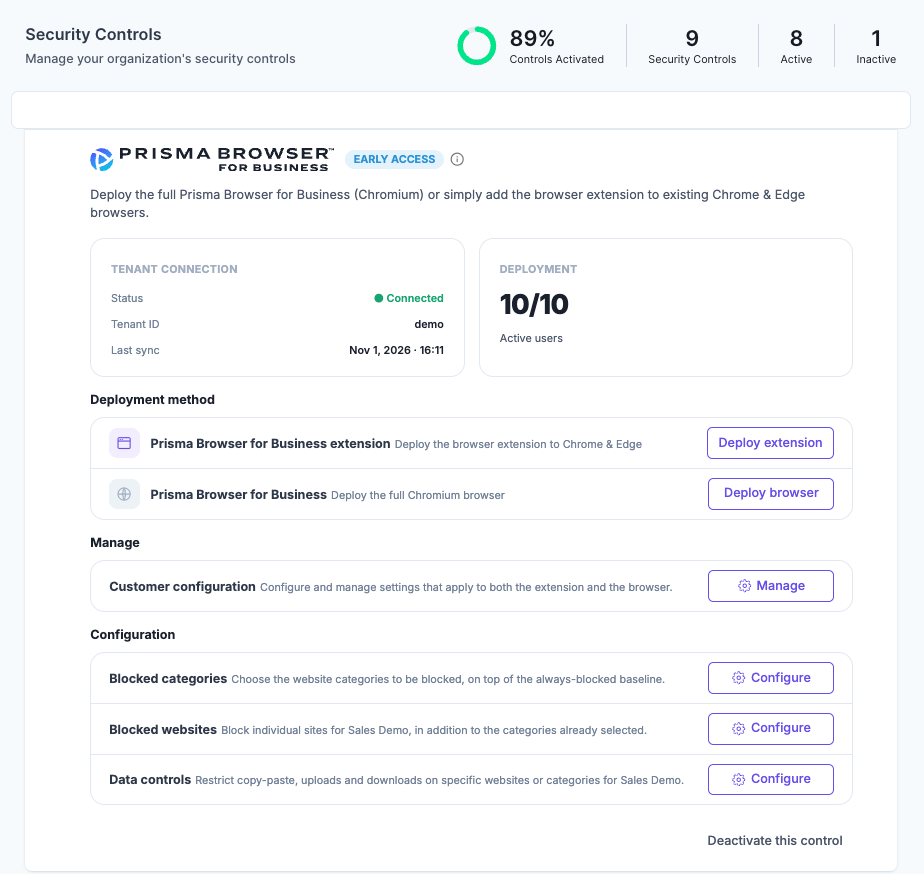
Every MSP is fielding questions about AI from their clients right now. This gives you a real answer instead of a policy memo. AI Usage and Control, powered by Palo Alto Networks, lets you set per-client rules on what moves into AI tools: restrict copying, pasting, uploading and downloading by website or by category. Sanction what the client has chosen and put guardrails around everything else.
The new AI usage report shows you which AI tools are actually in use per client across the browser, cloud and even endpoint. It paints a picture of who is using them and what risk that may create to drive business conversations with your clients.
Minutes, not a project
Protection starts preconfigured. Malicious site blocking, file scanning and malicious extension blocking are live the moment it lands. Pick the extension for the browsers people already use, or the standalone browser for Linux, unmanaged machines and anywhere protection should not depend on which browser someone opens.
“The rollout through our RMM was super smooth,” said Guardz early-access partner Kevin Kehoe of Datawise Networks. “Within minutes, the Prisma Browser for Business was on every device, including their Chrome and Edge profiles, and it was quick and easy to configure and deploy.”
The gap is closed
Email security stops the message. Identity protection watches the account. Endpoint protection catches what reaches the device. Each does its job well, and attacks still get through. That’s because the moment between the click and the compromise happens in the browser and nothing was there.
That gap is now covered by one of the best detection engines in the industry, delivered the way MSPs actually work. Browser Security is available now for MSPs in the U.S., included in Elite and available as an add-on to other plans.
This launch is for the U.S. only. Partners outside of the U.S. should contact your local Guardz team for more information.