MSP technology news headlines for the week of Nov. 2, 2026
A widespread M365 outage put MSPs on continuity duty this week, while Huntress uncovered a worm-like campaign using compromised ScreenConnect environments to spread rogue remote access tools. Meanwhile, N-able is urging customers to patch critical N-central vulnerabilities, Commvault is introducing new recovery capabilities for AI agents, and Sherweb is connecting cloud operations data to MSP automation through MCP. Fresh research also highlights growing cybersecurity demand, rising infrastructure costs and the challenges of keeping pace with AI-driven threats.
If you’re ready for more of this week’s MSP news and partner program updates, scroll on down!
Microsoft 365 outage disrupts Outlook, Teams and other cloud services
A global Microsoft 365 disruption affected email, collaboration, administration and security workflows as Microsoft worked to restore capacity across multiple regions.
Microsoft reported service degradation affecting Exchange Online and Microsoft 365 features beginning Nov. 12. Impacted functions included Outlook access and mail delivery, Teams features that depend on Exchange Online, Microsoft 365 Copilot, administrative portals and portions of Microsoft Defender for Office 365. Microsoft reported improving availability and reduced email queues on Nov. 13, although some users continued to experience intermittent access problems and delayed mail delivery. Follow the latest updates on the Microsoft 365 service health page.
➡️ Microsoft 365 outage stretches into second day, putting MSPs on continuity duty
Commvault gives IT and security an AI agent recovery plan
New AgentRecover capabilities are designed to help enterprises audit AI agent activity, restore agents and recover affected data and systems across Amazon Bedrock AgentCore and Microsoft Foundry.
Key quote from the press release:
“Business logic is moving out of applications and into agents, and agents don’t behave deterministically. A single agent decision can trigger changes across data, applications, and infrastructure on multiple platforms. Enterprises need to see and audit what agents have done, then recover both the agent and affected resources. That’s what we’re delivering for customers building on Amazon Bedrock AgentCore and Microsoft Foundry.” — Pranay Ahlawat, chief technology and AI officer, Commvault
N-able urges N-central customers to apply HF2 as security response continues
N-able says N-central 2026.4 HF2 addresses the highest-risk vulnerabilities disclosed this month, while additional fixes are planned in a follow-up hotfix.
Key facts from the security update include:
- N-able is urging customers with on-premises N-central deployments to install 2026.4 HF2 as soon as possible and keep servers inaccessible from the internet until the upgrade is complete.
- Hosted N-central servers have already been upgraded by N-able and returned to service, while all hosted and on-premises customers must also update their Agents and Probes.
- N-able says all identified vulnerabilities that could be exploited by an unauthenticated user have been addressed.
- Remaining vulnerabilities require an authenticated N-central account, often with elevated privileges, or additional conditions that limit exploitability and will be addressed in subsequent hotfixes.
Huntress warns SCKit worm is spreading rogue ScreenConnect clients across MSP environments
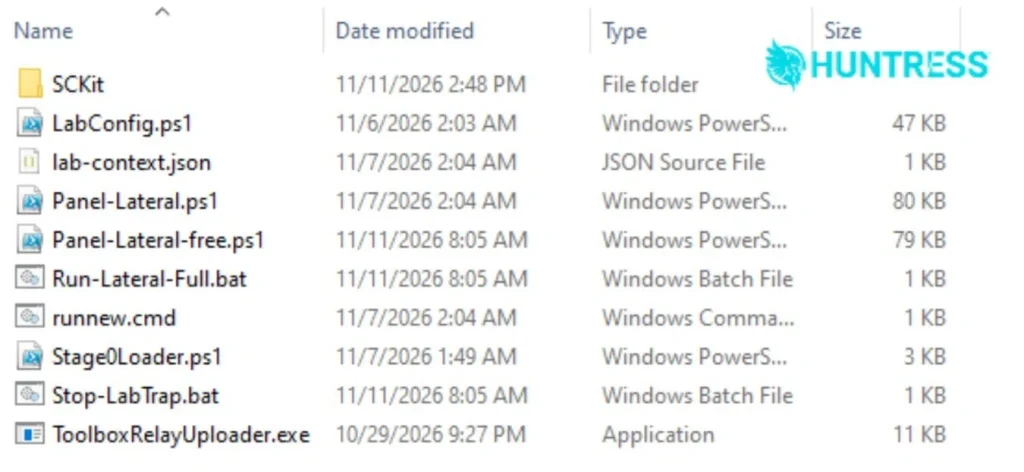
Huntress says attackers used compromised cloud-hosted ScreenConnect panels to deploy a custom toolkit across hundreds of managed endpoints, creating persistent access and attempting to steal technician session cookies.
Key findings from the report include:
- Huntress observed attackers using ScreenConnect Run commands to install rogue clients on at least 288 endpoints across 48 organizations.
- The activity appears linked to vulnerable versions of the third-party RMM+ extension, which could accept a blank access key if an administrator had never configured one.
- ConnectWise disabled five potentially associated third-party extensions across more than 400 partner environments as a precaution.
- The SCKit toolkit installs a second attacker-controlled ScreenConnect client, establishes persistence and attempts to intercept technician session cookies.
More headlines from Huntress
➡️ Huntress finds persistent webshells and cryptominers after AhsayCBS compromise
Coro adds services certification and public-sector opportunity program for partners
New programs give partners a path to deliver Coro services and identify U.S. public-sector opportunities.
Key quote from the press release:
“Every program we build starts with speaking to partners and building based on what they want and need. The days of building for the partner instead of with them are gone. Resale only takes partners so far. Services are where they build real margin. While SLED Miner brings them public-sector opportunities they’d otherwise spend hours hunting for, CCISP gives them the full services opportunity around Coro. Through hands-on training and real deployment experience, they can prepare to implement and manage the platform for customers over time.” — Heather Harlos, global VP of marketing, programs and enablement, Coro
Sherweb opens cloud operations data to MSP AI agents through MCP
The read-only MCP server connects approved AI tools with cloud subscription, usage, pricing and billing data.
Key quote from the press release:
“MSPs are already experimenting with AI, but its value depends on having access to the right business data at the right time. Our goal is to make Sherweb’s capabilities available wherever our partners choose to work, whether that’s an AI assistant, an automation platform or something they’ve built themselves. MCP gives us a standardized way to make that possible and creates the foundation for agents to play a much bigger role in MSP operations over time.” — Rick Stern, senior director of platform, Sherweb
GTIA finds North American service providers expanding cybersecurity and AI plans
North American service providers report rising cybersecurity demand alongside persistent customer control gaps.
Key findings from the report include:
- Seventy-six percent plan to add cybersecurity solutions in the next 12 months, compared with 65% in 2025.
- Fifty-one percent named AI-generated attacks as a leading concern.
- Only 42% said more than half of customers had MFA on all critical systems and 35% reported immutable air-gapped backups.
T-Mobile Business reaches technology advisers through CableFinder marketplaces
The integration adds T-Mobile connectivity qualification and pricing to marketplaces used by major technology services distributors.
Key quote from the press release:
“CableFinder is one step in a broader effort to change how T-Mobile works with partners. We’re meeting them where they already do business and removing friction along the way. It starts with connectivity because nothing works without it. By bringing T-Mobile Business Internet and SuperBroadband to CableFinder, we’re making it easier for partners to uncover new opportunities and turn a single conversation into long-term customer value. And when it’s easier to do business with T-Mobile, everyone has more opportunities to grow.” — Chris Jones, VP of ecosystems and partner alliances, T-Mobile Business Group
11:11 Systems report finds rising infrastructure costs and cyberattacks are top data center concerns
The 2027 State of IT Infrastructure Resilience study found IT leaders are grappling with higher infrastructure costs, persistent cyber risk and growing operational complexity as they plan for the year ahead.
Key findings from the report include:
- 90% of respondents said total data center infrastructure costs increased over the past 12 months, with an average year-over-year increase of 13%.
- 43% named cyberattacks as their top data center concern, while 73% expect data protection, backup and recovery budgets to increase in 2027.
- 69% of IT leaders experienced at least one cyberattack in the past 12 months, and 24% experienced three or more.
- 62% said the average cost of one hour of downtime exceeds $250,000.
Cowbell plans standalone AI liability coverage for U.S. small and midsize businesses
The non-admitted policy for U.S. small and midsize businesses is scheduled to become available Jan. 1, 2027.
Key quote from the press release:
“AI liability is no longer only about people using AI. It’s about AI agents acting on their own, with no human in the decision-making chain. When an agent goes rogue, a business can face its own losses and claims from customers and others at the same time. We designed Cowbell AI Liability Insurance for that agentic reality, giving brokers a concrete solution for their clients.” — Simon Hughes, chief commercial officer, Cowbell
ESET launches Threat Intelligence Investigation Lab
The new toolset combines IOC search and sample submission to help SOCs, government organizations, CERTs and MSSPs validate threats and accelerate incident triage.
Key quote from the press release:
“Security teams face suspicious IOCs and files every day and need fast, trusted, privacy-aware validation to determine the right next step. The goal is to help analysts answer the questions that matter most: Is this dangerous, where has it been seen, and what should we do next? Investigation Lab makes ESET telemetry more accessible to clients and enriches it with in-depth behavioral context, helping teams decide faster whether to block, investigate, escalate, or close an alert with greater confidence.” — Roman Kováč, chief research officer, ESET
Barracuda says third-party GitHub exposure led to XDR credential incident
Barracuda says a cloud access key exposed through a compromised third-party development environment enabled unauthorized access to portions of its internal cloud environment and systems tied to XDR integrations.
Key facts from the security advisory include:
- Barracuda confirmed the attacker obtained initial access through a cloud access key stored in a configuration file within a third party’s GitHub repository after that party’s development environment was compromised.
- The attacker had access to an affected system between Nov. 1 and Nov. 2 that stores credentials used by Barracuda XDR to collect data from connected services such as Microsoft 365, Google Workspace and endpoint security platforms.
- Barracuda says it found no direct evidence that customer integration credentials were viewed or accessed, but it notified potentially affected customers and advised them to revoke and recreate those credentials.
- The attacker searched for reusable credentials and cryptocurrency assets and used compromised credentials to move laterally within parts of the environment.
Azul survey finds Java patching lag behind AI-driven exploit expectations
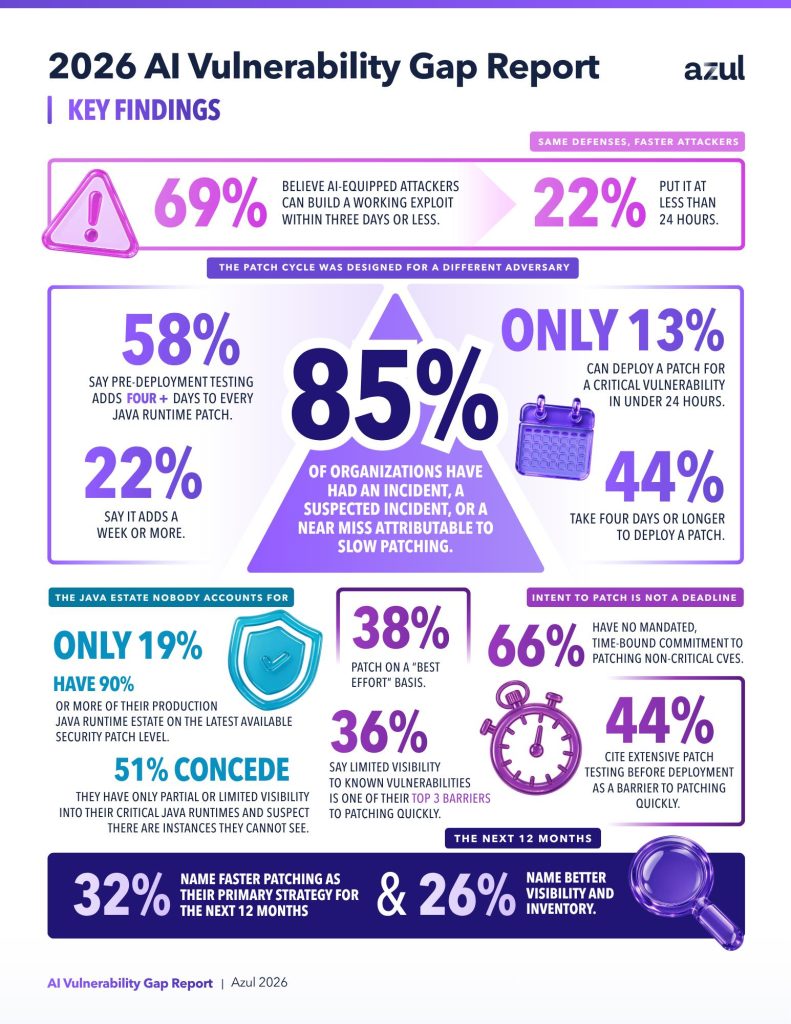
The survey finds a gap between expected AI-assisted exploit speed and critical Java patch deployment.
Key findings from the report include:
- Sixty-nine percent expect AI-enabled attackers to exploit a new vulnerability within three days or less.
- Fifty-six percent say they can deploy a critical patch within three days.
- Eighty-five percent report an incident, suspected incident or near miss tied to slow patching.
Matt Whitlock is ChannelPro’s tech editor, bringing more than 25 years of technology industry experience and a practical perspective on the tools and trends shaping the IT channel. A seasoned editor, podcast host and event moderator, he covers hardware, cybersecurity and emerging technologies with a focus on what they mean for IT service providers. Through product reviews, analysis and industry conversations, he helps MSPs and MSSPs separate useful innovation from marketing hype, with a little humor along the way.
Images: Huntress; 11:11 Systems; ESET; Azul